 alt Hacker News
ShinyHunters Extorted Boeing Spin-Off Prior to Arrests
Comments
A Jordanian teen is behind ShinyHunters? I don't know if this is impressive or just a sad commentary on the state of security at the organizations they ransomed.
I wouldn't leap to the conclusion that they have the right people; I would wait for evidence. They seem to have found them with incredible speed - how often has an attack been resolved this quickly? It would not be the first time the wrong person was arrested (and smeared) in a high pressure situation.
They need a head on a pike to save face for the FBI, both in front of the public and for internal credibility in government, law enforcement, and within their own origanization. Imagine how the FBI would look if they couldn't find or apprehend the perpetrators. And the current FBI - the leadership and their superiors, at least - seems much more focused on politics than predecessors.
interesting "rules of engagement" they have, including "no PRC companies"! :
https://krebsonsecurity.com/wp-content/uploads/2025/11/slsh-...
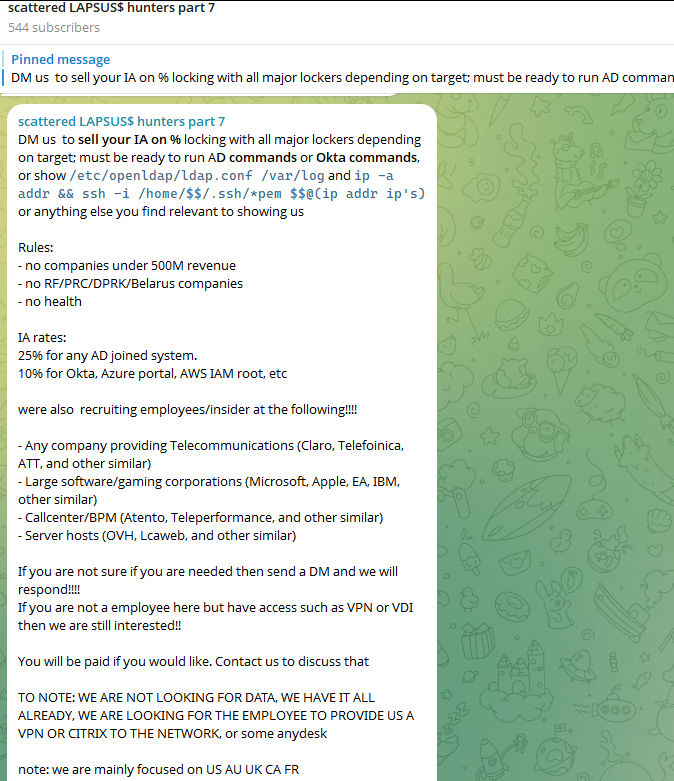
(from https://krebsonsecurity.com/2025/11/meet-rey-the-admin-of-sc... linked in the original post)
I support shinyhunters in all their endeavors.
I was never interested in hacking but as a software engineer with 15 years of experience, I frequently encounter tricky situations in the code where I think to myself that it would present a perfect hacking opportunity and probably present in a large percentage of software.
Last time I tried my hand at whitehat hacking on HackerOne, it took me 30 minutes to find a major system crash/DoS vulnerability in a major platform. The company acknowledged that the issue was real but denied me the bounty payment because they said I would have to 'prove' that it leads to catastrophic failure. I had already done so in the sense that you could reliably infer it from the data I had provided, but it seemed like they were baiting me into committing a felony (DoS attack) to prove my point, which I wasn't prepared to do but I'm sure I could have done cheaply. So yeah, whitehat hacking seems to be a waste of time. Most software today is incredibly insecure.