 alt Hacker News
>We know that Microsoft's bitlocker had at least one backdoor
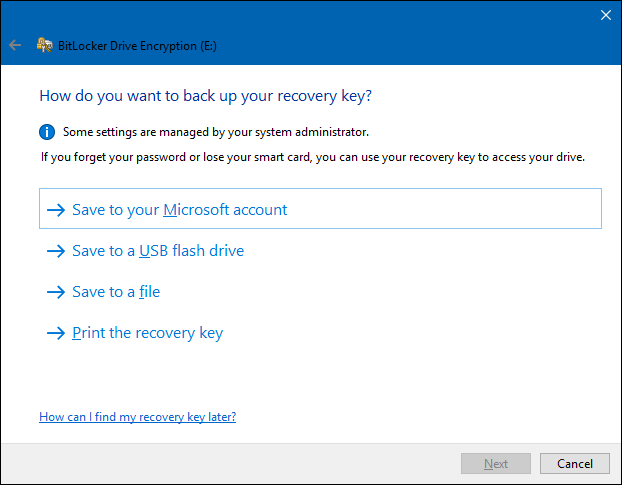
Source? The closest I found was microsoft's key escrow system, but that's hardly a "backdoor" given it's publicly documented, and it's explicitly stated in no uncertain terms when you're setting it up[1]
[1] https://static0.howtogeekimages.com/wordpress/wp-content/upl...
Look up YellowKey. Specifically crafted NTFS transaction logs would unlock any Bitlocker drive with transparent encryption. Some people believe it was an intentional backdoor, kind of a debated topic.
I'm not 100% certain either way.